Security · Štit
Stop attacks before they begin.
Štit sees an attack before it reaches you. Around it, a security team that covers your shifts, tests your defences every day and answers when it matters — on your infrastructure, under your rules.
Preemptive, not reactive
Get there before the attack does
Detection-and-response waits for the breach. Štit anticipates and disrupts attackers first — and it does it quietly, in the background.
Seamless
Integrates into your existing environment — no disruption, no downtime, no complex setup.
Operation-less
Runs autonomously. No constant manual monitoring or tuning to keep it effective.
Technician-less
No dedicated security team required to operate, maintain or watch over it.
How it works
Three moves: deceive, disrupt, deny
Deceive
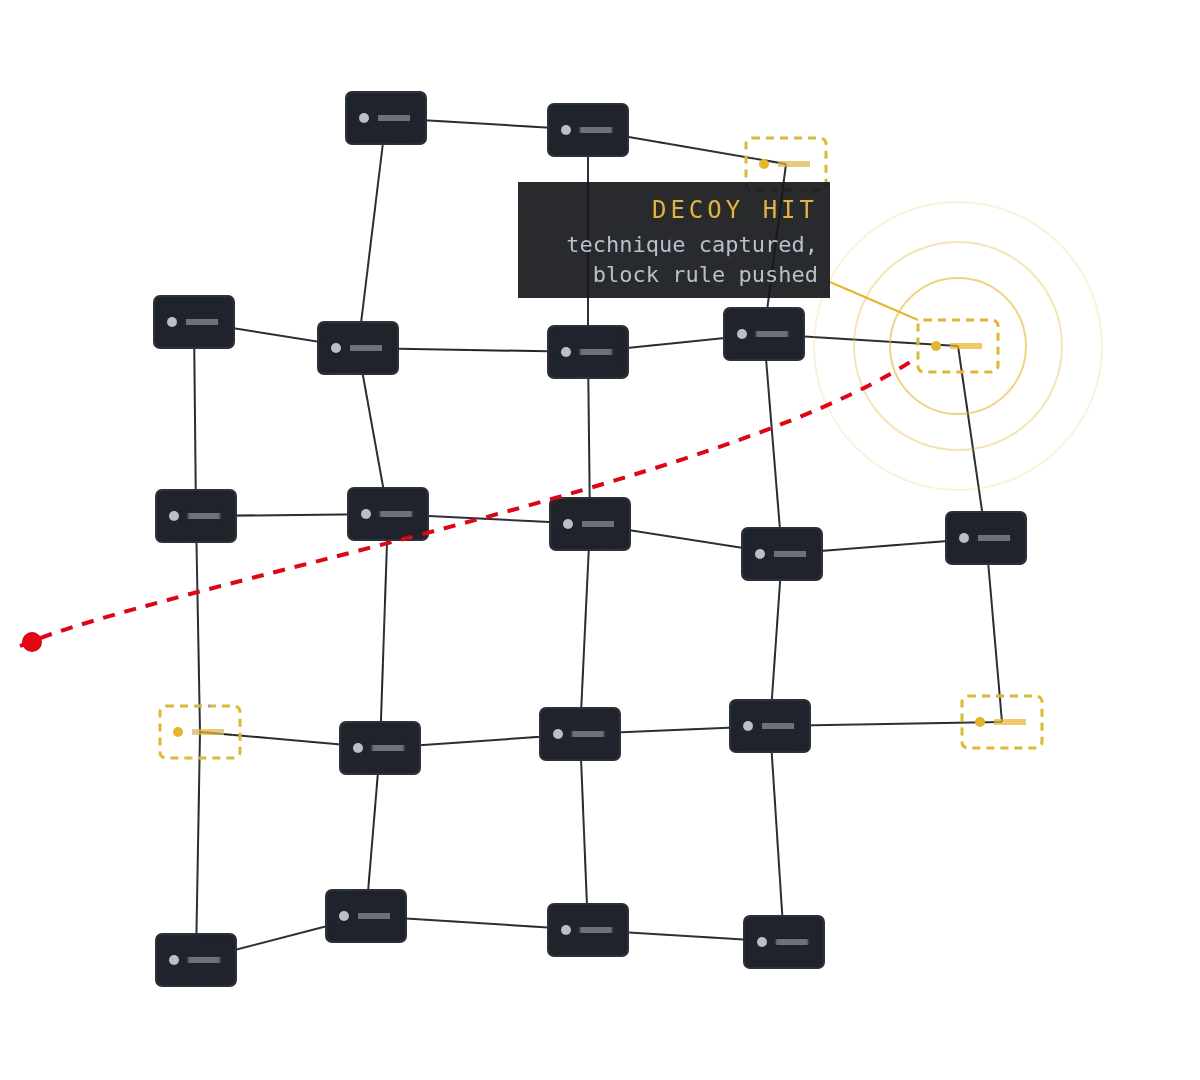
Patented, self-adapting cyber-clones of your portals, VPN access and devices fool even Shodan and Censys. A decoy has no legitimate use, so every touch is hostile — no false alarms, by definition.
Disrupt
Adaptive AI processes live attack data in real time, turns it into prevention and shares what 100+ trap nodes worldwide see, fast enough to catch zero-days.
Deny
Your real attack surface is obscured, and confirmed threats are blocked automatically through your existing firewalls and endpoint tools.
Track record
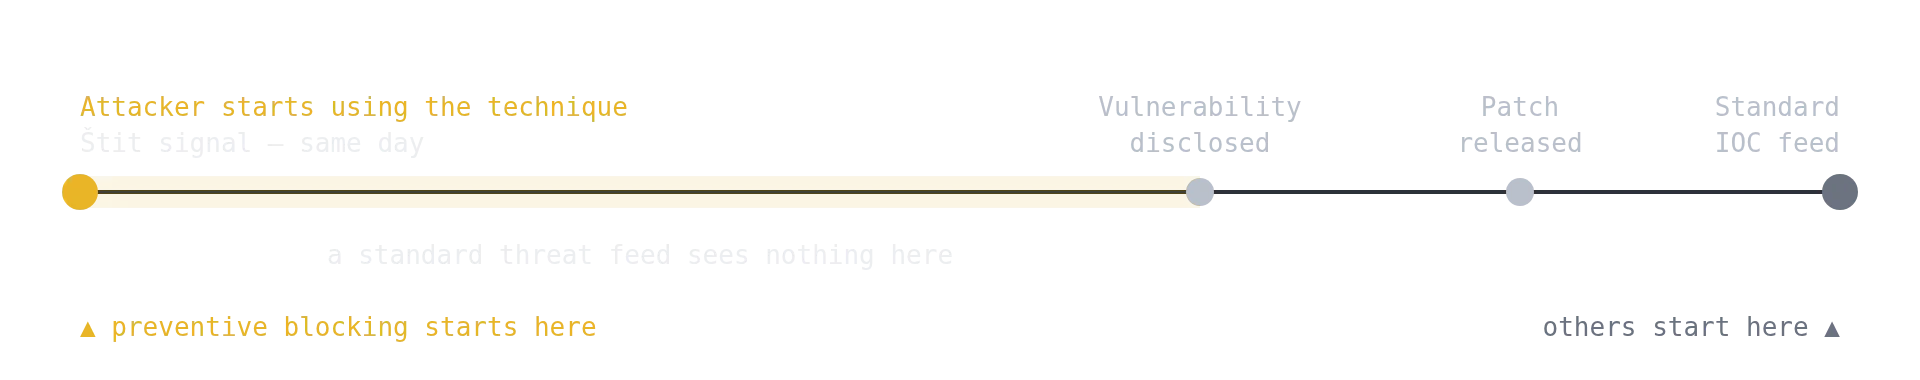
Zero-days caught before public disclosure
SharePoint
observed ~1 month before the 2025 disclosure
Oracle
detected ~1 month before the 2025 disclosure
Log4Shell
flagged on the day of public disclosure
Fits your stack
Works with the tools you already run
Štit pushes indicators straight into enforcement — your firewall, WAF and DNS layer — and into your SIEM as context, without waiting for anyone to approve a rule by hand. FortiGate, Palo Alto and Barracuda — and any next-generation firewall that reads an external threat feed. Delivered via REST API and STIX/TAXII, mapped to MITRE ATT&CK. Built for IT and OT / embedded / IoT environments, for governments, critical national infrastructure and enterprise.
Services
Four services. Your infrastructure stays yours.
The order follows the path of an attack: stop it before it arrives, see it the moment it gets in, prove the defence works, and have someone to call when none of that was enough. Each service works as an extension of your team.
Preemptive protection
Decoys that look like your systems signal an attack the day it starts — and push the indicators straight into your firewall, WAF and DNS layer. Included with 24/7 detection.
24/7 detection & response
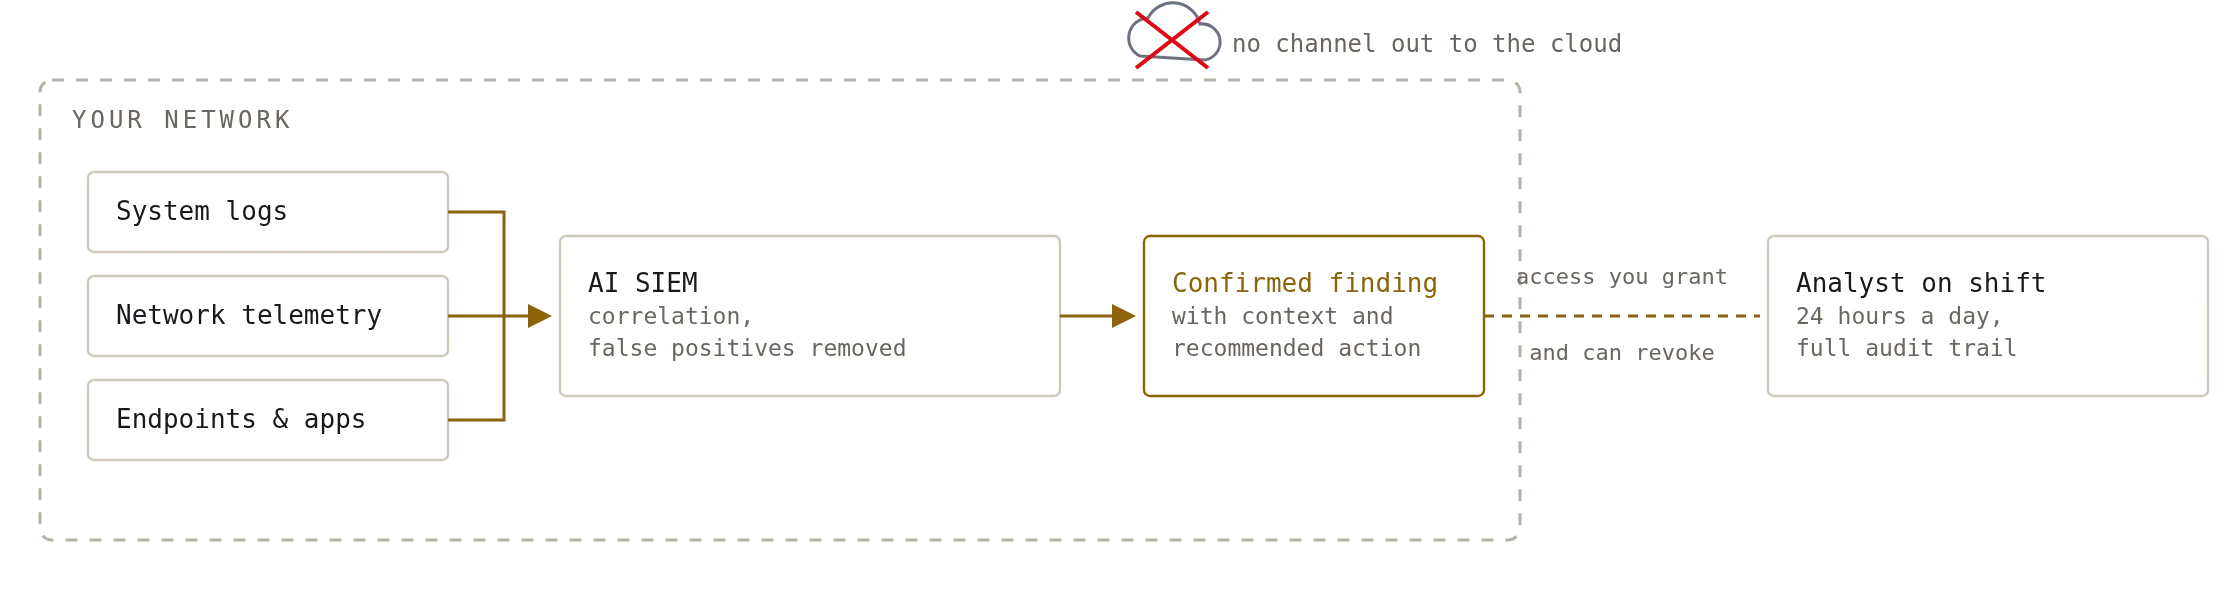
An AI security system on your premises collects and correlates events and discards false alarms on its own. Our analysts cover the shifts; you keep the decision on every action.
Continuous defence testing
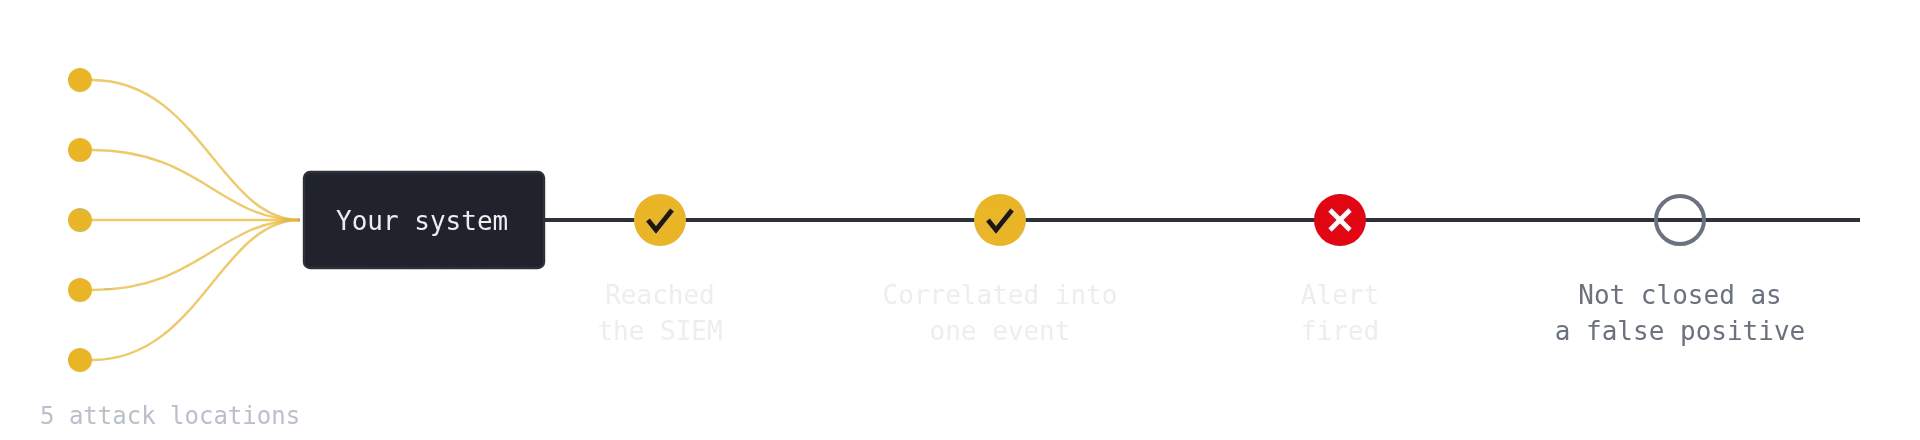
Attacks run continuously from five countries and are traced step by step through your SIEM, to show exactly where detection breaks. Plus leaked credentials, fake domains and a live map of what you expose.
Incident response team
Retained before you need it: activation within two hours, 24 hours a day. Forensics from day one, containment without shutting the business down, and help with DORA and NIS2 reporting.
How we work
Co-management, not outsourcing
Your data stays inside
The system runs on your premises. No cloud, no external log storage, nothing crosses your border. Analysts work through access you grant and can revoke, with a full audit trail.
Cost does not grow with data
No charge per GB or per event. Sources you switch off today because of licence cost can be switched back on, and the price stays the same for the whole contract.
No new tools to learn
We connect to the SIEM and log sources you already run — no migration, no replacement. The platform, the rules and the data stay yours; your team sees exactly what we see.
See it live
See Štit catch a threat — live.
1 day
first decoys live, from ready-made templates
3–7 days
clones of your own internal applications
2 weeks
first testing baseline from all five locations
30 days
detection running in parallel with your team, measured by the alerts you no longer handle by hand
One 45-minute conversation, no preparation on your side. We walk through what Štit and the services look like in your environment — then a proof of value on your own systems. No changes to production at any step.
Services
Four services. Your infrastructure stays yours.
The order follows the path of an attack: stop it before it arrives, see it the moment it gets in, prove the defence works, and have someone to call when none of that was enough. Each service works as an extension of your team.
Preemptive protection
Decoys that look like your systems signal an attack the day it starts — and push the indicators straight into your firewall, WAF and DNS layer. Included with 24/7 detection.
24/7 detection & response
An AI security system on your premises collects and correlates events and discards false alarms on its own. Our analysts cover the shifts; you keep the decision on every action.
Continuous defence testing
Attacks run continuously from five countries and are traced step by step through your SIEM, to show exactly where detection breaks. Plus leaked credentials, fake domains and a live map of what you expose.
Incident response team
Retained before you need it: activation within two hours, 24 hours a day. Forensics from day one, containment without shutting the business down, and help with DORA and NIS2 reporting.
How we work
Co-management, not outsourcing
Your data stays inside
The system runs on your premises. No cloud, no external log storage, nothing crosses your border. Analysts work through access you grant and can revoke, with a full audit trail.
Cost does not grow with data
No charge per GB or per event. Sources you switch off today because of licence cost can be switched back on, and the price stays the same for the whole contract.
No new tools to learn
We connect to the SIEM and log sources you already run — no migration, no replacement. The platform, the rules and the data stay yours; your team sees exactly what we see.
See it live
See Štit catch a threat — live.
1 day
first decoys live, from ready-made templates
3–7 days
clones of your own internal applications
2 weeks
first testing baseline from all five locations
30 days
detection running in parallel with your team, measured by the alerts you no longer handle by hand
One 45-minute conversation, no preparation on your side. We walk through what Štit and the services look like in your environment — then a proof of value on your own systems. No changes to production at any step.